IntrudeRaven simulates real-world attacker behavior to discover, validate, and demonstrate attack paths across your ecosystem—autonomously, securely, and continuously.
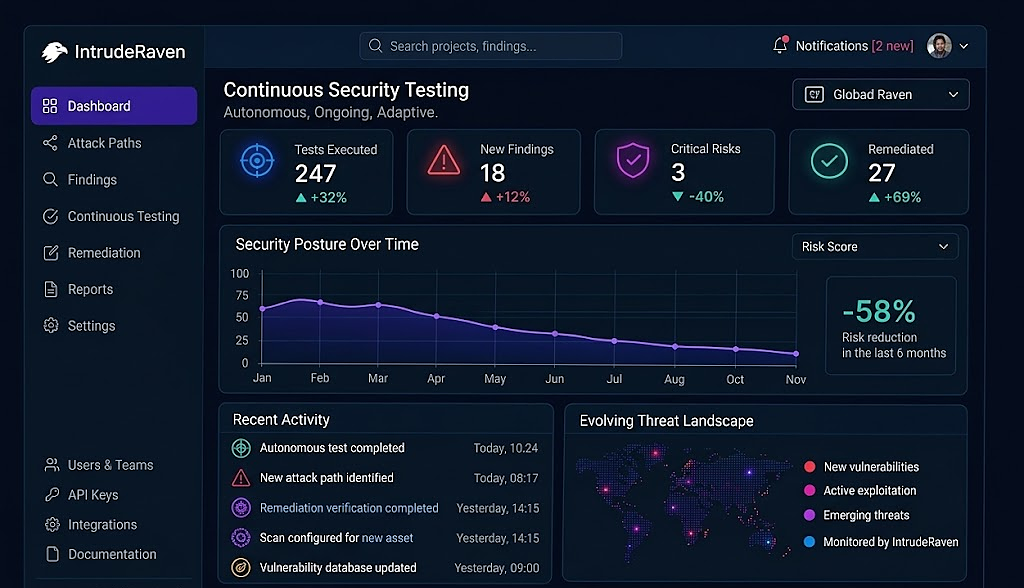
Organizations evolve constantly: new servers, new apps, new configurations, and new vulnerabilities. Point-in-time tests leave blind spots between assessments. IntrudeRaven turns pentesting into a continuous, evidence-driven process without operational friction.
IntrudeRaven autonomously analyzes, correlates, and explores your ecosystem, reconstructing the exact journey an attacker could take.
Combines machine learning techniques, graph theory, and specialized security LLMs to identify viable attack paths with automated validation and actionable insights.
Assessments with zero knowledge or authenticated access.
Comprehensive scanning across networks, cloud, apps, and identities.
Natural language explanations contextualized for business stakeholders.
Visualizing interconnected vulnerabilities, exploits, and lateral movement.
Contextual risk metrics prioritized by real-world business impact.
Specific, actionable guidance tailored to your exact stack.
IntrudeRaven automatically generates dedicated report streams with full technical rigor tailored to every stakeholder.
Makes adaptive decisions, discovers paths, and validates without constant human guidance.
Every finding includes reproducible proof and contextual validation.
Correlates vulnerabilities, credentials, and live permissions.
Continuously exercises and shrinks your attack surface over time.
IntrudeRaven is a sovereign European solution, engineered in Portugal by CryoBeeAI with a clear focus on European compliance, high agility, and enterprise resilience.

Strict European regulatory compliance with full GDPR adherence.

Local cybersecurity engineering team with same-timezone support.
Scalable licensing designed for fast-growing SMEs to enterprises.
Pragmatic tech addressing actual security challenges.
IntrudeRaven validates your security posture continuously, backing compliance mandates with verifiable technical proof.
Technical evidence for risk management and security posture verification.
Continuous operational resilience testing and recurring assessments.
Continuous technical vulnerability assessment and lifecycle tracking.
Verifiable offensive testing for critical payment card environments.
Helping enterprises and public entities stay ahead of modern threat actors.
IntrudeRaven provided crisp clarity on our perimeter exposures and allowed us to respond quickly. The engineering support is stellar.
Finally a cybersecurity solution built for realistic SME needs. Frictionless deployment and immediate value.
We highly value Portuguese engineering proximity and European data privacy standards. A true trusted partner.
Technical analyses, offensive security advisories and newsletter editions published regularly by the CryoBeeAI specialists.
How European organizations can use continuous autonomous pentesting to prove the effectiveness of the technical controls required by NIS2.
In this first issue, we look at why traditional CVSS-only prioritization fails and how graph correlation reduces real risk.
We launched new autonomous modules for inspecting and testing configurations across multi-cloud environments and hybrid architectures.
Schedule a live demo to see how IntrudeRaven lowers real exposure with verified evidence.